In financial services, a system failure is never just an IT problem.
It is a compliance event, a reputational event and a revenue event simultaneously. We manage the technology environments that South African financial institutions cannot afford to lose.
What we hear most often.
The specific technology and compliance burdens this sector carries.
A network outage is a compliance event, a reputational event and a revenue event at the same time.
SARB cyber resilience assessments require continuous documentation that most in-house teams cannot sustain.
FSCA CPD evidence is assembled manually by compliance officers in the weeks before submission deadlines.
Mid-tier institutions lack the budget for a fully staffed 24/7 SOC, leaving them exposed.
Branch network incidents go unresolved for months because carrier escalations are not managed systematically.
POPIA breach notification timelines create liability when incident response processes are undocumented.
What we do about it.
Specific capabilities, deployed against the challenges this sector faces.
24/7 SOC that speaks SARB fluently
Our managed Security Operations Centre provides mid-tier banks and insurers with enterprise-grade detection and response. Powered by Microsoft Sentinel. Aligned to SARB Directive 1 of 2018.
One partner. Every branch. No excuses.
We manage retail banking networks as a single portfolio — monitoring every link, managing carrier escalations and maintaining failover configurations.
FSCA CPD evidence. Automatically.
EDVantage generates FSCA-ready CPD evidence and B-BBEE Element 6 reports automatically as advisers complete their programmes. No more February panic.
Proprietary productPOPIA compliance consulting
Documentation, governance frameworks and audit-ready evidence aligned to the Information Regulator's expectations. Section 22 breach notification processes built in.
ISO 27001 certified operations
Every managed security engagement operates under our ISO 27001 certification. Audit evidence is generated as a natural output of our service delivery.
PCI-DSS network segmentation
Network architecture designed for PCI-DSS compliance. Segmentation, monitoring and change management aligned to card industry standards.
We know the regulations.
We have been working within them for years, across every sector we serve.
SARB Directive 1 of 2018
Cyber resilience framework requirements built into how we design and operate SOC services.
FSCA CPD obligations
EDVantage automates FSCA CPD evidence generation throughout the year — not assembled retrospectively.
POPIA
Data governance frameworks, breach notification processes and Section 22 compliance built into service delivery.
PCI-DSS
Network segmentation, monitoring and change management aligned to Payment Card Industry standards.
ISO 27001
Our managed cybersecurity operations are independently certified under ISO 27001.
B-BBEE Level 1
Maximum preference points in every FSI procurement evaluation. Highest rating available.
We built Sourceworx around the realities of this market: its regulation, its infrastructure and its pace.
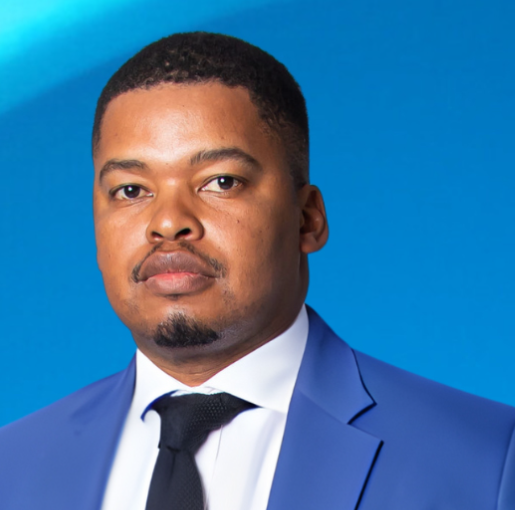
Masande Dyasi
Managing Director
Thought leadership for Financial Services.
Research, analysis and practical guidance written for your sector.
Not sure where to start?
Run our free diagnostic tool and get a personalised technology readiness report for your organisation.
Ready to talk about your environment?
Tell us what you are dealing with. We will tell you exactly how we would respond.
Start the conversation