OT/IT Convergence Security in South African Mining: Protecting Production Without Disrupting It
How to architect secure boundaries between operational technology and corporate IT networks, preserving production data flows while blocking cyber threats from crossing into SCADA and ICS environments.
+ About the author
Sizwe Sourceworx
Head of Insights, Sourceworx
Sizwe leads thought leadership and content strategy at Sourceworx, writing on managed IT, cybersecurity, compliance and the operational realities facing mid-market organisations across South Africa.
Certifications
ISO 9001 · 27001 · 20000
Based in
Johannesburg, South Africa
The convergence of operational technology and information technology networks is one of the most significant shifts in the South African mining industry. SCADA systems, PLCs, sensors and historian databases that once operated in complete isolation from the corporate network are now connected, delivering enormous value in production monitoring, predictive maintenance and remote diagnostics, while simultaneously creating a category of cyber risk that the mining industry is only beginning to understand.
The Threat Landscape for OT Environments
OT environments in mining face a fundamentally different threat profile than corporate IT environments. The consequences of a successful attack are not measured in data loss or reputational damage: they are measured in production hours, safety incidents and potentially in lives. A ransomware infection that shuts down a plant control system, a targeted attack that manipulates sensor readings to cause equipment damage, or a simple misconfiguration that allows a corporate malware infection to reach the SCADA network are not theoretical risks. They have occurred at mining operations globally.
The Industrial DMZ Architecture
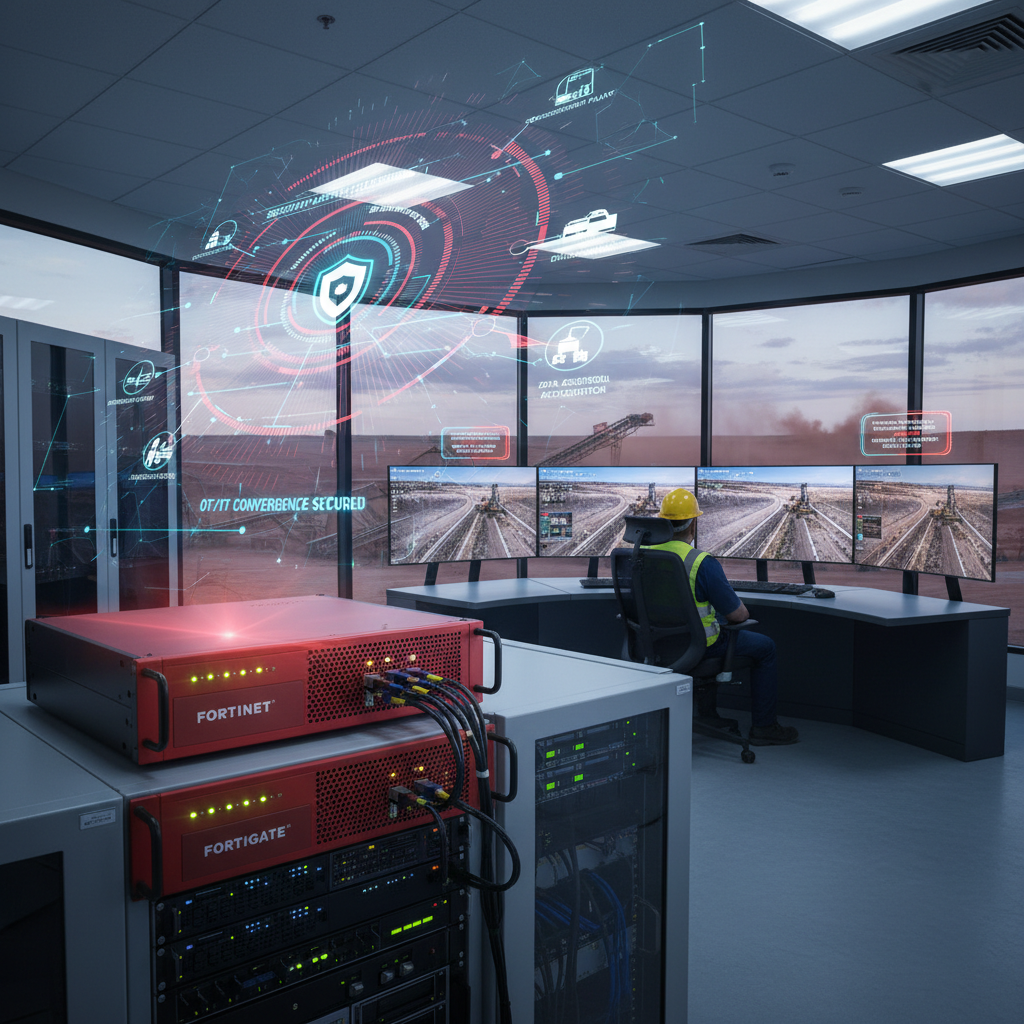
The foundation of secure OT/IT convergence is the industrial demilitarised zone: a network boundary that allows operational data to flow from OT systems to corporate systems for business intelligence and reporting purposes, while preventing any traffic from flowing in the opposite direction without explicit inspection and approval. This boundary must be enforced by industrial-grade firewalls with policies designed for the specific protocol characteristics of SCADA and PLC communications.
Fortinet's Industrial Security Platform
Sourceworx deploys Fortinet's FortiGate industrial security platform for OT/IT convergence environments. The platform provides deep packet inspection for industrial protocols including Modbus, DNP3 and IEC 61850, combined with the enterprise security capabilities of the broader Fortinet Security Fabric.
Implementation Approach
Phase 1: OT asset discovery and network mapping. Phase 2: Risk assessment and architecture design. Phase 3: Industrial DMZ implementation. Phase 4: SOC monitoring extension to cover OT environment. Phase 5: Ongoing vulnerability management and security testing.
Ready to act on this?
Our team can give you a specific assessment of where your organisation stands — in a single conversation.
Download WhitepaperTake the diagnostic
See where your organisation stands — before the next pressure point arrives.
Start assessmentRelated reading
Topical right now
Speak to a specialist.
No slide decks. No generic proposals. A conversation about your environment, your sector and your priorities.
Talk to our team